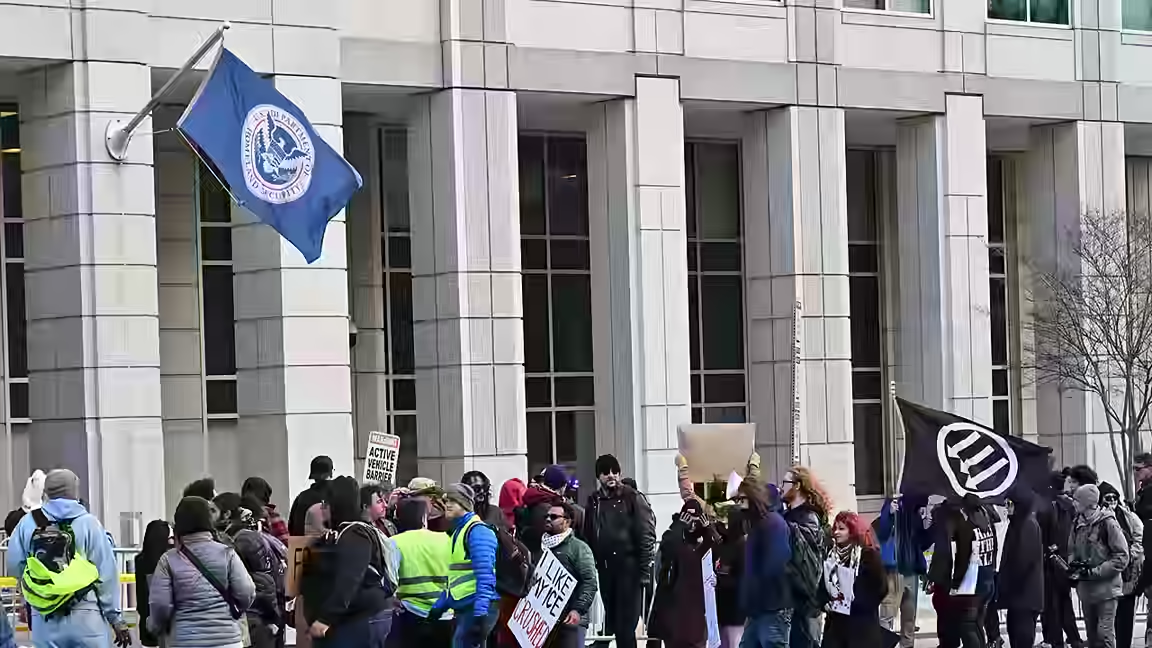
Privacy-focused hosting provider FlokiNET said on October 29 that it rejected a takedown notice concerning Icepick, a website publishing the professional identities and roles of US immigration-enforcement personnel. The company said the request came from ZeroFox, a security contractor acting for a government agency with which the Iceland-based provider has no relationship.
FlokiNET's account presents the dispute as a test of how infrastructure companies distinguish public-interest reporting from harassment. The notice described the site as a doxxing campaign, according to the provider. FlokiNET rejected that characterization, arguing that Icepick focused on work identities, agency roles and professional contact information rather than home addresses or private-life details.
That assessment is FlokiNET's position, not an independent finding. The provider acknowledged that the underlying data originated in a breach and that the people listed did not consent to its collection. It nevertheless concluded that the site could serve journalists and citizens examining the exercise of public authority. The supplied evidence does not include the original takedown notice, a response from ICE or ZeroFox, or an independent review of every field published by Icepick.
The hosting decision did not keep the original domain reachable. FlokiNET said the icepi.cx domain stopped resolving after registrar CentralNic placed it on serverHold. The provider reported that the site later returned under icepicx.is through a different registrar. This sequence illustrates the number of companies able to affect availability: a host may reject a request while a registrar or registry takes separate action.
FlokiNET also linked the request to a Department of Homeland Security contract with ZeroFox covering ICE and Homeland Security Investigations. It said the contract allows the contractor to file notices for the department through 2028. The provider argued that automated detection cannot by itself resolve whether published material serves accountability reporting or creates unacceptable personal risk.
The company called for greater transparency in notices filed on behalf of public agencies. Its proposed safeguards include identifying the client, stating the legal basis, naming the party accountable for errors and disclosing when automated systems produced the alert. Those recommendations reflect the provider's policy view rather than an existing legal determination in this case.
The dispute leaves substantial issues unresolved, including the precise content of the contractor's complaint and the registrar's basis for suspending the first domain. It nonetheless documents how a government-linked removal effort can move through multiple private infrastructure layers, with different intermediaries reaching different conclusions about the same site.